Local Accounts Management
Time-Limited, Just-in-Time Privileged Access
Local administrator accounts are a necessary but dangerous part of endpoint management. Traditional approaches—shared passwords or static solutions—leave standing privileges that attackers can exploit. Lockfy Enterprise transforms local account security with time-limited, just-in-time access that eliminates standing privileges and provides complete audit trails.
How It Works
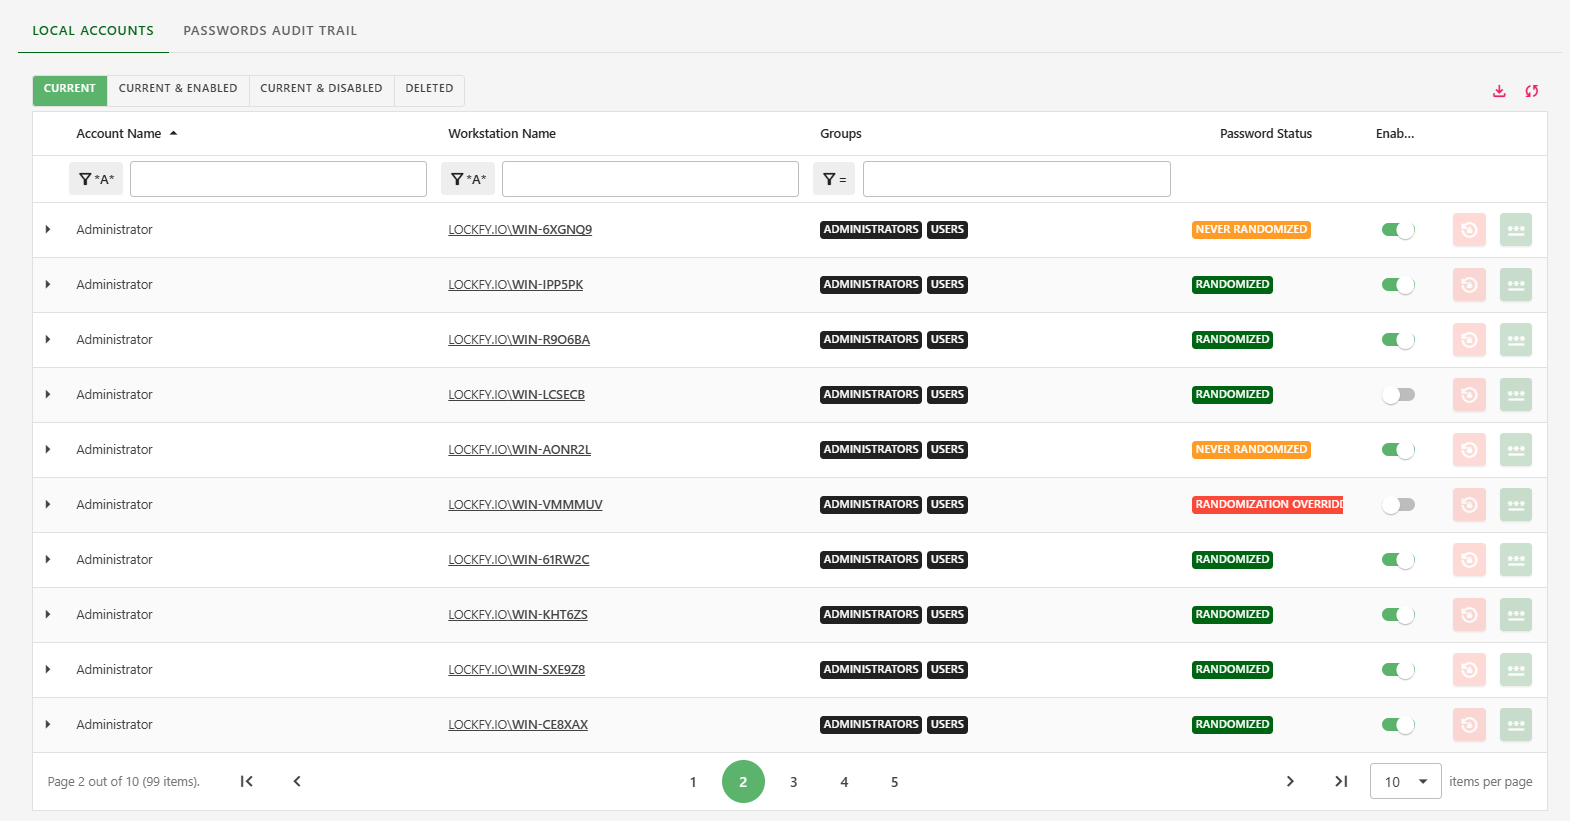
Lockfy centralizes local account management with an automated, time-bound model that ensures privileged access is only available when actively needed.
| Capability | Description |
|---|---|
| Centralized Management | Manage all local accounts across the organization from a single console |
| Automated Password Randomization | Local admin passwords are automatically randomized and managed centrally |
| Time-Limited Access | Generate temporary passwords with specified access duration (e.g., 30 minutes, 2 hours, one shift) |
| Automatic Revocation | Upon expiration, Lockfy automatically signs the user out and randomizes the password again |
| Local Account Inventory | Complete view of all local accounts and group memberships across managed workstations |
| Group Membership Visibility | See which local accounts belong to Administrators, Users, and other privileged groups |
The Lockfy Process
Lockfy replaces standing privileged credentials with a secure, time-bound access model:
| Step | Action |
|---|---|
| 1 | Randomize — Local admin passwords are automatically randomized and managed centrally |
| 2 | Request — When access is required, authorized personnel generate a temporary password and specify the exact duration needed |
| 3 | Access — The user logs in with the time-limited credential |
| 4 | Revoke — Upon expiration, Lockfy automatically signs the user out and randomizes the password again |
Comparison: Traditional vs. Lockfy
| Approach | Security Posture |
|---|---|
| Shared Passwords | High risk — passwords are shared, rarely changed, and often known by multiple former employees |
| Traditional Solutions | Improved but incomplete — passwords rotate but access is not time-bound; once access is granted, it remains until manually revoked |
| Lockfy Enterprise | Best-in-class — time-limited, just-in-time access with automatic revocation and full audit trails |
Key Benefits
| Benefit | Impact |
|---|---|
| Eliminate Standing Privileges | No permanent local admin credentials exist to be compromised |
| Prevent Lateral Movement | Attackers cannot use compromised local credentials to move across the network |
| Control Vendor Access | Third-party vendors receive time-limited access that expires automatically |
| Complete Audit Trail | Every privileged access request and session is logged for forensic investigation |
| Simplify Compliance | Meet regulatory requirements for privileged access management and auditability |
Use Cases
| Scenario | Application |
|---|---|
| Vendor Maintenance | Provide equipment vendor with 2-hour local admin access for scheduled maintenance—access expires automatically |
| Emergency Response | IT team generates 30-minute temporary password for emergency troubleshooting |
| Shift-Based Access | Maintenance team receives time-limited credentials valid only for their shift |
| Field Technician Access | Remote technicians receive time-bound credentials for site visits—access expires after the visit |
| Privileged Account Auditing | Complete record of who requested access, when, for how long, and what actions were taken |
Ready to Eliminate Standing Privileges?
Learn how Lockfy Enterprise can transform local account security with time-limited, just-in-time access.
Contact our team to schedule a demo.
Ready to Protect Your Workstations?
Book a DemoLearn how Lockfy Enterprise can provide always-on protection for your organization.